July 10, 2026
Read Case
Executive Decision Overview
When projects conclude, secondary teams frequently require access to design files, calculation sheets, and historical decision logs to inform subsequent initiatives. Leaving raw working directories open invites accidental modification, whereas locking assets behind individual creator credentials stalls dependent workflows. This decision brief outlines the protocol for converting closed team workspaces into structured, cataloged read-only assets across functional silos.
Read-Only Tier
Default Inter-Team State
RBAC Auditing
Central Access Governance
99.4%
Retrieval SLA Target
Zero Drift
Immutable Baseline Guarantee
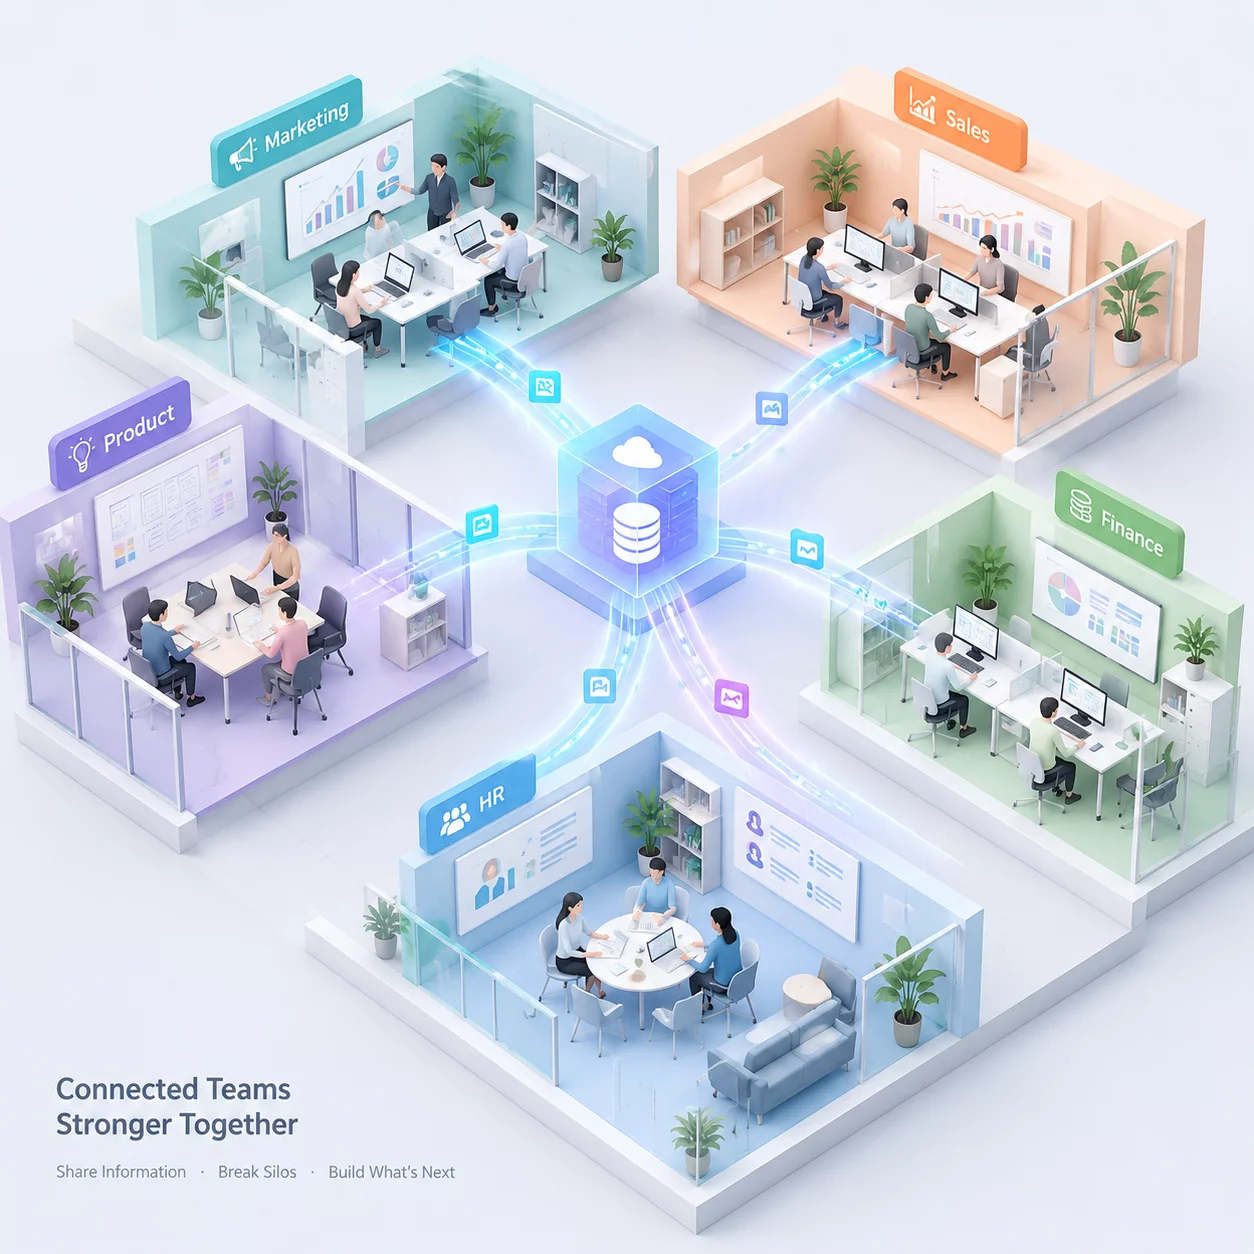
Standardized inter-departmental access mesh for archived project repositories.
ARCH-GRID-REF #702
1
Stage 1 • Boundary Analysis
Identifying Inter-Departmental Asset Dependencies
Product and engineering initiatives rarely exist in complete isolation. As soon as a sprint cycle or delivery milestone concludes, upstream analytics, marketing, and client support teams consistently search for baseline documentation to justify operational updates.
Project leads must audit which deliverables contain shared intellectual value before decommissioning the workspace. Creating explicit manifest records prevents subsequent ad-hoc access requests from interrupting former team members.
- Enumerate all cross-functional artifacts including specifications, schemas, and contract summaries.
- Separate confidential client records from general reusable technical patterns.
Organizational Guidelines
Need Custom Archive Governance Frameworks?
Explore our full decision library on project ownership changes, asset retrieval, and long-term document organization.
2
Stage 2 • Permission Topology
Transitioning from Read-Write to Governed Read-Only
Active collaborators naturally operate with write and modify permissions during delivery. However, retaining unrestricted write permissions after project closure is the leading cause of accidental file corruption and undocumented revisions.
The archive transition process systematically strips individual modification privileges and assigns group-level read permissions. This ensures every employee within adjacent departments can browse and clone assets without risking the source of truth.
Critical Protocol Rule
Never grant individual direct write access to finalized archive directories. All post-closure modifications require a version fork approved by the records administrator.
Implementing role-based access control (RBAC) groups tied to organizational directories ensures permission updates happen automatically when personnel transition between teams.
3
Stage 3 • Discoverability & Indexing
Establishing Common Cataloging Metadata
Unsearchable archives result in duplicate work across departments. To make cross-team access useful, completed-project materials must carry uniform indexing tags describing the project scope, technical stack, date of retirement, and original team leads.
Automated repository indexes broadcast available documentation packages to the central knowledge portal, enabling engineers in parallel branches to locate historical solutions within minutes.
- Standardize top-level README files with architecture summaries and historical contact rosters.
- Implement searchable metadata attributes across cloud storage buckets and intranet portals.
4
Stage 4 • Periodic Access Review
Sustaining Long-Term Document Organization & Compliance
Archive access policies must not remain static. Security requirements, regulatory compliance standards, and storage tiering rules change over time, necessitating annual access audits across all cross-team repositories.
Regular reviews ensure obsolete guest tokens are revoked, high-traffic documentation is elevated to prominent catalog categories, and sensitive historical records remain safeguarded against unauthorized extraction.
Clarifications
Frequently Asked Questions
Further Decisions
Browse Full Decision Base
Related Decision Protocols
Peer Commentary
Active Thread
Archival Review Debriefs
Submit Archival Feedback
Contribute your analysis to this project record preservation log.
To leave a comment, please log in to your account.
No comments yet. Be the first to submit feedback on this decision record.